Breaking

Tuesday, March 5, 2019

March 05, 2019

Donald Trump Urges United States to be the first to Launch 6G Network

The United States President, Donald Trump may not be a man you like, but the truth is you must agree that he’s never boring or previsible. He always have a new idea on his mind running, never thinking of its consequences or consistencies behind it.

After lifting up the idea of creating the first Space Force to police the galaxy, the President now wants his country to develop 6G as soon as possible. Trump used his Twitter to state that he wants 5G and even 6G in the United States as soon as possible, since it is far more powerful, faster, and smarter than the current 4G LTE standard.

He endorses that American companies should step up their efforts now, or they will be left behind by the rest of the competition.
The 5G network will slowly roll out in the U.S. this year and the first smartphone to arrive in the market with this technology will be the Galaxy S10 5G, which will be available this summer. The download speed of the 5G network is expected to be 20 times faster than 4G LTE.

The new faster speed will allow the creation of new services and businesses and will give more strength to existant segments like video streaming service. When coming to 6G, despite some internal talks of the start of development of this new technology, there are no 6G standards for now, and it’s too soon to even talk about it. The United States President continued its speech by saying:
Currently, Huawei is the leader of the segment, being followed by Nokia, Ericsson, and ZTE. Despite the lack of basis behind some comments of the President, this isn’t a bad idea, after all, more competition will expand the offer for consumers, thus not allowing a monopoly or control over a new technology that will represent another important step for the future of the Mobile industry.

News Source

Thursday, February 14, 2019

February 14, 2019

Google Releases Password Checkup & Cross Account Protection

Google has released two updates to mark Safer Internet Day which would protect user data, including usernames and passwords. One of them is a neat extension for the desktop version of Chrome, while the other is called Cross Account Protection.

Google has gathered a massive dump of 4 billion compromised credentials to keep your username and account safe from hackers and attacks. When you install the extension called Password Checkup, it matches the data you’ve shared with Google with the one typed in and tells you if any of the entries was hacked. If it suspects any of your entries to be hacked, it will trigger an automatic warning and suggest changing your password.

There are needs to protect your usernames and passwords especially the ones getting into your Google Account, gj if you store card data, accounts for online banking and other sensitive information. Some protections haven’t extended to the app you use for Google Sign In, so Cross Account Protection comes in handy.

 According to Google "We built Password Checkup so that no one, including Google, can learn your account details. To do this, we developed privacy-protecting techniques with the help of cryptography researchers at both Google and Stanford University."

 Password Checkup is a Chrome extension that will detect whether the username and password you’re using to login to an online account or service have been stolen. If either has, an alert will pop up in your browser, advising you of the breach and suggesting you change your password.

 Although Google can implement protections if you’re using its services and it thinks you’ve been hacked, before the introduction of Cross Account Protection, Google was unable to implement the same security processes. However, now it will share any breach data with the third party, so they can take action, such as forcing you to re-login.

 But instead of leaking all kinds of sensitive information, the breached host will only know the fact of security event happening and when that occurred. The feature was developed with Adobe, Internet Engineering Task Force, and Open ID Foundation.

Wednesday, February 13, 2019

February 13, 2019

How To Improve Email Security

Email security, improve email security, how to improve email security
Image from Pixabay
Despite the emergence of countless digital communication channels, especially social media networks, the significance of email has not died down. That, and the fact that usage of email keeps growing on a daily basis, even going so far as to be a necessary requirement when creating most online accounts, goes to show just how important email is. However, just as its significance and usage increases, so too do the threats that plaque it, especially with regard to cybersecurity. Imagine what a devastating blow it would be if all the information contained in your email was exposed, including sensitive information such as the login credentials to various websites and your financial information. Since email security is paramount, we aim to explore various ways to improve it.

  Employ the use of SSL/TLS
One of the most significant security threats to email is man-in-the-middle attacks, where hackers intercept your emails. The risk increases exponentially when the hackers decide to hack the individual instead of the system and send you emails. The best way to prevent man-in-the-middle attacks of this nature is to make use of SSS/TLS, both of which are encryption protocols that protect the information shared between the computer and a server as well as between two or more servers. SSL/TLS encryption prevents the emails from being intercepted while in transit between the various servers and systems.

  Encrypt your email
Although SSL/TLS encryption protects your emails from interception, it does not protect the email messages directly. Therefore, it is important to have that extra layer of security by encrypting your email. This guarantees that even if the email is intercepted, it still remains secure without exposing the information contained within. While there are plenty of plugins and email encryption software out there, we recommend using OpenPGP, otherwise known as GNU Privacy Guard (GPG). The software encrypts your email in a way that guarantees that only the sender and the recipient can access it. Both the sender and the recipient have access to a keypair – both public and private. The public key is interchangeable and responsible for the encryption, while the private key is always fixed and is responsible for decrypting the emails. 

  Exercise caution when opening emails
Hackers have a tendency of using emails to send malware through emails. Often, they do this by sending email attachments and links with messages that appeal to your interests. For instance, you could receive an email about a free holiday urging you to click on a link to find out more. Therefore, you should treat all suspicious emails with caution, particularly when dealing with spam. As long as you don’t know the sender of the email, you should be cautious about opening it. Nevertheless, hackers aren’t the only threat you should be concerned about when using your email. Companies have a tendency to send tracking links to monitor the click and open rate of their emails. Compared to the malware issue, this might not sound like much of a problem. However, these tracking links compromise your privacy and expose your habits, which is just as much of a problem as hacking.

  Make use of multiple email accounts
As mentioned before, there’s an increase in the significance and usage of email. As such, it is not uncommon to find people using a single email account for various purposes. Unfortunately, that is much like putting all your eggs in one basket and increases the risk of being compromised. Therefore, we advise making use of multiple email accounts for different purposes. For instance, you can split your accounts to handle banking/finances, work/business, and social media. Doing this reduces the risk of exposure and increases the chances of you detecting when something is out of order. For instance, when you receive non-financial information to your financial email account, you can tell that it is suspicious and take appropriate measures. 

  The Takeaway
While the methods listed in this article may not be the only way to improve email security, they are some of the most important, especially when it comes to encryption. Nevertheless, you should make sure to read more about improving email security and employ as many methods as possible to guarantee better protection of your email accounts.

Tuesday, February 12, 2019

February 12, 2019

BuyPower.Ng: How To Setup And Buy Power From BuyPower.Ng

BuyPower online payment service lets you purchase electricity units (tokens) instantaneously anywhere, anytime in Nigeria by making use of your internet-enabled smart phone or computer. It saves you from queuing and time wasting whenever you want to recharge your pre-paid meter in Nigeria. 


You can start making use of the service by visiting www.buypower.ng or by making use of buypower app for Android. Internet connection is needed for you to be able to make use of the service.
The interesting part of it is that, you can buy electricity units for your loved ones at buypower.ng i.e if the prepaid meter is not registered in your name, you can still make payment to get the token to be recharged on the pre-paid meter. All you need to have handy, is the pre-paid meter number.

How To Buy PrePaid Meter Units Online In Nigeria At BuyPower.Ng

  • Type the url buypower.ng in a browser [ Laptop, phone, Tablet or Desktop ]
  • If you do not have an account on the platform click on the “register button” on the home page and enter your details on the next page.
  • If you have an account on the platform click on the “login button” on the home page and enter your login details.
  • Once you login through any of the methods mentioned above, you would be taken to the order page.
  • On the Order page, Enter your Meter Number, the Amount you want to purchase, and select the payment method.
  • You would be taken to a confirmation page to check that the meter no and other details are valid.
  • You would need to check that you accept the terms and conditions in order to proceed.
  • Once you click confirm, you would be redirected to the payment gateway to enter your payment details.
  • If payment is successful, you would be taken back to buypower.ng where your token would be generated and displayed. It will also be sent to you via sms and email.
  • Enter the token on your prepaid meter as required. Once recharged, the units purchased will be added to the available units on the prepaid meter.
That’s all.

How Much In Naira Is Electricity Units Per KWh in Nigeria?

As at 19th of May 2018, buypower.ng was purchased @

29.81 N/KWh

.

Monday, February 11, 2019

February 11, 2019

PROMO!! Get Your Responsible And Mobile Friendly Blog Today


The main reason for writing this post is to encourage the young bloggers or those that have passion for blogging to be more optimistic and courageous about their decision.
 Don't allow what the bad-mouthed ones will say to stop you from taking part in what you have passion to. Always be enthusiastic about your passion.

 That's by the way, now let's go to the main business of the day.  I'm offering a blog promo for anyone that is interested to have a nice looking and responsibe blog at a very pocket friendly amount (whether Blogspot or WordPress blog but the price varies)..

Both blogs will be built with friendly optimized optimizes.

 For a blogspot blog: the price is just N6000 If you already have one and wants to redesign it, the price is N3000

 For WordPress blog: the price is N8000 (provided that you have your domain and hosting) If you already have one and wants to redesign it, the price is N4000.

 Your blog will be live in 3 - 5 days unless stated otherwise. I believe this is the best blog promo you have seen before.

 I know what will be running in your mind now is: how do I get in touch with you? Alright, I know you can't afford to miss this awesome opportunity. 

Contact me on:
Email: thebigga9@gmail.com
Phone & Whatsapp on: 09050965432
 Happy blogging in advance!!!

Friday, February 8, 2019

February 08, 2019

FIFA Road To World Cup: The Best Sports Video Game

Sports games by their nature don’t turn up for each new season as entirely fresh products. The economics of the industry have determined that they re-use the same engine and models for years at a time, which means the difference between them can often be limited to current uniforms, a few new features and some adjustments to ball physics. And those changes are usually influenced as much by fan feedback as they are by the development teams working on them.FIFA 98,the best sports video game,
So it’s tough looking at say Madden 18 as something entirely separate, since its creation was heavily influenced by the sales and reception of Madden 17, and it will in turn play a big part in how Madden 19 is designed.

How do you pick one of those games and say, ok, THIS ONE is the best, when much of what made it great may have been inspired by—or come directly from—an entirely different video game?

Then you have to take into account the way sports games have changed their entire outlook over the last 20 years. In the 90s, series like FIFA and NBA Live were perfectly happy being fast, accessible, almost arcadey.

Fast forward to today and advances in technology have turned blockbuster sports games into simulations, each one trying its hardest to replicate the on-field experience as best it can (or, if it can’t, then the broadcast experience instead). This makes direct comparisons between games in long-running series pretty damn hard!


Making matters worse is that each sport is different, with its own set of fans, style of play and culture. What makes the #1 baseball game better than the #1 hockey game? Is football better than basketball?


So after lingering over a short list of truly great sports games—Madden 2002, NBA 2K11, Pro Evolution 6, NBA Jam, NFL 2K5—I’ve settled the tie by going with one that wasn’t just a very good sports game in its own right, but one which decided to give fans everything they could have wanted or needed for years to come, all in the one box.

The game I'm talking about all this while is nothing but the great FIFA: Road to World Cup 98, as bizarre but beloved a major sports game as I think we’re ever going to see.
At the time of its release in 1997, it was a damn fine football game. It had very flash polygonal visuals, audio commentary, all the things we’ve long associated as being hallmarks of the FIFA series. But it’s where the game went above and beyond what we expect of a sports game can include, whether at the time or today, that marks it as truly great.

INDOOR FOOTBALL - In addition to regular 11v11 football, FIFA 98 also included an entirely separate 5v5 indoor mode, with its own rules and conditions, like the fact the ball never went out of bounds. It was just as fun as the actual FIFA. Maybe more fun. And while it had actually been introduced in FIFA 97, the fact it stuck around in 98 when there was so much else in the box is one of the things that helped cement this game’s legacy.

AN ACTUAL WORLD CUP - The reason for the game’s longer title was the fact that the development team decided to include, alongside domestic leagues, the 1998 World Cup. Not just the finals in France, but the entire qualifying system as well. That meant over 170 nations and their squads made it into the game, an absolutely ridiculous number that literally represented every football-playing country on Earth at the time (modern FIFA games usually only include a few dozen). You could, if you wanted, play as one of the smallest nations on the planet, take them all the way through qualifying then win the tournament itself, a feat so monumental that after FIFA 98 it would only be seen again in standalone video games specifically made for World Cups.


CUSTOMISATION: Besides the 170+ national teams, there were almost 200 club sides included in the game as well. And you could customise the lot. Home kits, away kits, even a player’s appearance. I remember spending what must have been weeks tinkering with this, making sure that every major team’s kit matched its actual design, and that player haircuts had been accurately recreated. This wasn’t just useful in 1997, either; people were playing FIFA 98 for years to come because as 1998, then 1999 rolled around, you could just update the kit designs again.

Here’s the most incredible thing about all this: FIFA 98 was so big it made another of EA’s own video games completely pointless. In addition to FIFA 98 (released in 1997), EA Sports had a game in development designed to cash in on the World Cup itself, due for release in early 1998. Simply called World Cup 1998, it had official branding throughout, from the tournament mascot to branded kits (a first for the series). But with only 40 teams, what was the point of buying it it when you could just fire up FIFA 98, edit some kits and enjoy much the same experience?

To get non-FIFA fans up to speed on just how crazy this was, it’s like NBA 2K18 shipping on four blu-rays, or the next MLB game deciding to include the entire Japanese and Korean pro leagues, just for one year, just for the hell of it.
This kind of thing just isn’t supposed to happen with sports games, because it gives fans everything they need to not buy your game the next year. Yet here we have, for one beautiful year, EA sports giving away the keys to the kingdom. Amongst the blur of year-to-year releases, FIFA 98's largesse looms large like no other sports game’s inclusions ever have.

But it’s not just the excess content that’s helped FIFA 98 endure. Quantity would be nothing without quality, and the game includes several other series favourites, from the humble free kick arrow (still somehow superior to anything EA comes up with these days) to the ability to slide tackle a goalkeeper and get instantly sent off, which despite its punishment ranks as one of the most cathartic moves in all of video games.
Then there’s the matter of the game’s soundtrack, beginning with its intro, perhaps the most iconic in sports game history:

Don’t let Blur’s cameo overshadow the game’s real musical hook, though, which is the fact much of the menu music was provided by The Crystal Method:

Sports games using popular music is nothing new today, but in 1997 it was a coup for FIFA (for reference, check out FIFA 97's tragic attempts at hip-hop and rock). Indeed, you could trace the series’ current place on the pop culture landscape back to IFA 98 and its soundtrack, which dared to suggest that, hey, maybe these sports video games can be cool.

In a world where sports games are and always have been seen as disposable, FIFA 98 stands apart. By including so many teams across such a breadth of competition, and allowing for such a degree of customisation, people were able to dig in and play it not just throughout 1997, but well into the next few years as well.

Even today, when the FIFA series is known as much for its licensing as it is its football and has over 20 years of experience under its belt, you’ll find fans still talking about FIFA 98 in reverent tones. Amazing what some decent music, tiny teams and the ability to let try and murder a goalkeeper will do to a fanbase...

Thursday, July 12, 2018

July 12, 2018

Google Plans to Incorporate Duplex into Call Centre Industry


According to a report from The Information, Google may be considering licensing Duplex to call centers and telemarketers. An anonymous source that claims to be close with Google's plans says that the company is already in talks with at least one firm that would like to use Duplex for “simple, straightforward customer service calls.” The interested company remains unnamed, but it is reported to be a large insurance company.
Gizmodo contacted Google, which provided a statement neither denying nor confirming the claim directly.
“We’re currently focused on consumer use cases for the Duplex technology where we can help people get things done, rather than applying it to potential enterprise use cases. We aren’t testing Duplex with any enterprise clients. Duplex is designed to operate in very specific use cases, and currently we’re focused on testing with restaurant reservations, hair salon booking, and holiday hours with a limited set of trusted testers. It’s important that we get the experience right, and we’re taking a slow and measured approach as we incorporate learnings and feedback from our tests.”
While Google's statement indicates that it is more concerned with personal voice assistant applications right now, it does not rule out pursuing enterprise customers in the future.

Applying Google Duplex in call centers could be very lucrative for the search giant. According to numbers from market analysts at Research And Markets, the cloud-based customer service market reached $6.8 billion in 2017 and is expected to reach $21 billion by 2020. In fact, other companies like Amazon have already started working on cloud-based voice services to offer to companies wishing to automate simple customer service requests.
Of course, there are a few negative implications of this move. Obviously, human telemarketers and customer service personnel will be displaced, which could mean the loss of 1.2 million jobs.
There is also the fact that consumers, in general, do not like dealing with automated customer service systems. According to a 2015 survey, 90 percent of those calling into service centers wish to speak to a human. Another 80 percent say they rush through automated systems just to get to a live rep.
Read more tech updates @ Gobuzz

Tuesday, July 10, 2018

July 10, 2018

Intel Core may leave Extreme Edition

Intel is going to kill off its Extreme Edition processor branding according to a long time former employee. What once was a badge of true bragging rights is about to be eliminated once and for all.
Intel may drop extreme Edition

According to a report from Tech spot, enthusiasts have enjoyed pushing the limits of processors practically since they became available to regular everyday users. Back in the days of Intel Inside commercials and a serious round of competition with AMD, Extreme Edition processors were released with huge price tags so that bragging rights were difficult to obtain.

Intel has used Extreme Edition branding since the first dual core CPU, a 3.2GHz Pentium D based on a 90nm process. Following up the Pentium D, the Core 2 Extreme series was released. Arriving closer to the present, the introduction of Intel Core with i7 Extreme Edition variants kept the same pattern.

Despite dropping Extreme from product titles, there may not actually be all that much changing. The introduction of Core i9 processors has essentially taken the place of extreme edition CPUs. Core i9 options still have the needed overclocking capabilities and certainly have extreme pricing that keeps them only in the hands of enthusiasts or those running a business where time is money.
July 10, 2018

"Docs" is protected despite Russian issue - Said Google

docs is protected

Russian search engine Yandex claims that it has been indexing private files from Google Docs, but the American firm says everything is a-okay. The alleged documents have not been validated, but Yandex stopped indexing Google Docs completely until the matter gets sorted out.
On Wednesday, Russia’s leading search engine Yandex, notified Google about a potential data breach after its users reported finding dozens of what appeared to be private documents turning up in searches.

According to the news from Tech Spot, Yandex spokesman Ilya Grabovsky said users were reporting that they were finding Google Docs files in arbitrary searches. The documents, which included an internal memo from a Russian bank, press summaries, and business plans, started flooding social media platforms in the country. The authenticity of the documents is so far unconfirmed.

“Yandex search only yields files that don't require logins or passwords,” Grabovsky said. Adding that the files were turning up in other search engines as well but not naming any specifically.

Within hours of the first reports, Yandex stopped producing links to Google Docs altogether and notified Google.
“Google Documents is a highly protected tool for joint work and it is working correctly.”
After a brief investigation, Google released a statement Thursday claiming that everything was functioning properly.
“Saving and protecting users’ personal data is our main priority,” the search giant said. “Google Documents is a highly protected tool for joint work and it is working correctly.”

The company explains that search engines can only index documents that have been "deliberately made public" by the authors. Users must make a conscious decision to open a file to indexing. It sees no issues with the way Docs is working internally, and all data should be private by default.

Thursday, July 5, 2018

July 05, 2018

WAEC 2018 May/June Result Is Out - How To Check Result

This is to inform the general public and especially, candidates that participated in the 2018 May/June West African Senior School Certificate Examination, WASSCE that their results are now available online.
2018 WAEC SSCE Results have been successfully uploaded online and it is accessible from the WAEC official result checking website. Candidates need to purchase the WAEC result checker which cost N500 (Five hundred Naira only) from authorized dealers or any WAEC office nearest to them to be able to access their results.

How To Check 2018 MAY/JUNE WAEC SSCE Result Online


  • Go to WAEC result checking portal www.waecdirect.org
  • Enter your 10-digit WAEC Examination Number. (This is your 7-Digit centre number followed by your 3-digit candidate number eg. 4123456789)
  • Enter the 4 digits of your Examination Year eg. 2018
  • Select the Type of Examination i.e. SCHOOL CANDIDATE RESULT
  • Enter the Card Serial Number found on the reverse side of your Scratch card.
  • Enter the Personal Identification Number (PIN) on your Scratch card
  • Click Submit and wait for your result to window pop out.

  • How To Check 2018 WAEC SSCE May/June Result Via SMS

    To check your 2018 WAEC result with your phone via SMS , use the shortcode format below:
    • Send WAEC*ExamNo*PIN*ExamYear To short-code 32327 (MTN, Airtel & Glo subscribers)
    For example -: WAEC*4250101001*123456789012*2013
    The SMS Costs N30 Only, so ensure that you have up to N30 in your phone before sending the SMS.
    Make sure to follow the format above. There should be no space in the message.
    Wait for your result to be delivered to your phone via SMS.
    Note: you can only use your result checker 5 times, so be wise!

    Thursday, June 21, 2018

    June 21, 2018

    Google Launches Android Podcast App

    Google has launched its own podcast app

    google launches Android podcast app
    Google Podcast App

    Google Podcasts is a very simple podcasting app. Users can search and subscribe to podcasts and Google includes a fairly robust library of podcasts so you’ll find almost anything here. Once you are subscribed, videos can be downloaded for offline playback or you just stream the videos online. It will also use AI to learn from your listening history and suggests podcasts you might like.

    However, the Podcasting app is yet to receive the reception Google might actually expected as it’s current rating is just 3.7/5 on Play Store.

    Apparently, most reviewers believe that Google’s new app lacks a lot of features that other apps have. For example, the app lacks the ability to create playlists, an auto-download feature, inability to mark multiple podcast episodes as played, and many more.

    Google Podcasts covers all the basics in a quick and compelling way. It’s nowhere near as full-featured as a podcast app like Pocket Casts , but it’s a great option if you don’t want to deal with a lot of setup or are just getting started in the magical world of podcasting. Also, it’s free to use.

    Tuesday, June 19, 2018

    June 19, 2018

    What facebook knows about you


    Facebook had to publicly revealed how it handles user data following the Cambridge Analytica revelations and Europe’s new strict privacy laws. This information came to you from a 229-page document Facebook submitted to the US Congress, it lays out in typed form what Mark Zuckerberg testified to at his April grilling.

    With some help from Business Insider, a shorter version that showed a couple of bits that may or may not be public knowledge yet was given.
    For example, you probably know that Facebook (and any smartphone application for that matter) knows about your Operating system, browser, carrier or ISP, and your IP Address.
    Here are some of them outlined below:
    • Mouse movements: Facebook records your mouse movements to distinguish you from a robot.
    • Browser Window: Another way Facebook distinguishes that you’re human is by monitoring whether your browser window is “foregrounded or backgrounded.”
    • Device information: Facebook also collects data about your devices, including your battery level, signal strength, available storage space, file names and types and plug-ins.
    • Network: Facebook also knows your mobile operator, internet service provider, and IP address, as well as your cookie data, time zone, and internet connection speed.
    • Device signals: The company also tracks Bluetooth signals and information about nearby Wi-Fi access points, beacons and cell towers.
    • Nearby devices: According to Facebook “in some cases, information about other devices that are nearby or on their network, so we can do things like help them stream a video from their phone to their TV”.
    • Data from device settings: Facebook tracks user’s GPS location, camera or photos if the permission for these have been given by a user. Call logs and SMS log history are also recorded if users choose to sync their Android devices or upload data.
    • Purchases: Data about your “online and offline actions” and purchases from third-party providers is collected, in addition to information about the “games, apps, or accounts” people use.
    If you would like to read the full Facebook response to Congress, CLICK HERE. now.

    Sunday, June 17, 2018

    June 17, 2018

    Apple set to close iPhone security loophole used by hackers and police

    Apple says it will change the default settings of its iPhone to stop hackers and law enforcement agencies to unlock devices without legal approval.
    Apple company, iPhone, iPhone security, Apple set to close iPhone security loophole used by hackers and police

    The Apple company has announced that a forthcoming software update will fix a vulnerability that allowed data to be transferred via the iPhone’s Lightning port without legal authorisation.

    The move will also make it more difficult for police to unlock handsets without authorisation.
    However, Apple denied the changes were designed to thwart US law enforcement. The company has been a prominent opponent of US legislation to force technology companies to maintain access to users' communications.

    In the update, the iPhone’s Lightning port will disable data transfer functionality. Once the device locks, nothing would be transferred from it unless the user’s password is entered first. Before, a loophole meant it was theoretically possible to access a handset’s data at any time using specialist ‘cracking’ software or hardware.
    Police forces made use of the ‘flaw’ to glean evidence and background information from phones for use in criminal investigations, but weren’t required to attain authorisation.

    “We’re constantly strengthening the security protections in every Apple product to help customers defend against hackers, identity thieves and intrusions into their personal data. We have the greatest respect for law enforcement, and we don’t design our security improvements to frustrate their efforts to do their jobs,” Said Apple.

    The changes to the default settings of the iPhone are intended to stop unauthorised access to the phones via the USB port without full legal authorisation.

    Friday, June 15, 2018

    June 15, 2018

    Top 8 Hardest Special Forces In The World

    Special Forces refer to military units who receive special training for the purpose of carrying out special operations. According to NATO, special operations can be described as “Military activities which are conducted by specially designated, organized, trained and equipped forces manned with selected personnel, using unconventional tactics, techniques and modes of employment”. This covers essentially, the duties performed by Special Forces.

    The duties carried out by these Special Forces vary from nation to nation and may include operations such as airborne operations, counter-terrorism, counter-insurgency, Covert Ops, Foreign Internal defense, Direct action, Hostage rescue, High-value targets/manhunting, mobility operations, intelligence operations as well as unconventional warfare, etc.
    Below are the top 8 special forces in the world in 2018

    TOP 8 SPECIAL FORCES IN THE WORLD

    • 1. THE UNITED KINGDOM’S GURKHAS:

    THE UNITED KINGDOM’S GURKHAS- hardest special training forces in the world
    For the people of Nepal who aspire to join this British military organization, the first set of punishing tests that qualify them for the actual military training are somewhat tame and involve having to do about 800 meters in 2 minutes or maybe 12 pull-ups.
    The actual training is much more difficult than anything dealt with by SAS trainees. The aspiring members are made to run 5 kilometers all the while saddled with a weight weighing 25 kilograms. The 25 kilometers incline upwards every 400 meters, and these aspiring members have to complete it in 48 minutes. This among others made their training to be the hardest special training forces in the world.
    • 2. PAKISTANI SPECIAL SERVICES GROUP:

    PAKISTANI SPECIAL SERVICES GROUP
    PAKISTANI SPECIAL SERVICES GROUP
    Coming second on the list of hardest special forces training in the world – Those eligible for selection into the SSG must have first served in the regular army and afterward have to pass an aptitude test as well with a score of 100.
    During the eight months of training, the men are required repeatedly, to cover a distance of 36 miles in 12 hours only. After that, they 5 miles run to finish in 40 minutes while saddled with a full pack.
    Once the 8-month period elapses, the real danger begins. The members have to perform 7 para drops, with 5 of them occurring during the day and the other 2 at night. Understand that skydiving at night has a ten-time higher chance of resulting in injury than during the day. After this, members are almost at their goal and have to spend a half year engaged in commando training after which they can finally join SSG.
    Also, it should be mentioned that for no reason other than health reasons, can one leave the organization.
    • 3. SPECIAL AIR SERVICES UK:

    hardest special forces training in the world
    SPECIAL AIR SERVICES UK- Among The Hardest Special Forces Training In The World
    Aspiring members of this unit are left in the middle of nowhere, saddled with a sixty-pound weight and rifle, with nothing by way of sustenance except a bottle of water and are instructed to cover a distance of 40 miles in under 20 hours. It is important to note that their boots and uniforms are purposely chosen to not be a good fit for them. Any police met on the way will attempt to capture them leading to their disqualification. Those who are able to meet up with the time frame also have to meet up with the 4-mile run in 30 minutes which follows.
    This training known as the Endurance became known worldwide when it so happened that 3 aspiring members died during the training process. Unfortunately, deaths are not at all strange for the exercise.
    • 4. THE PEOPLE’S LIBERATION ARMY, CHINA:

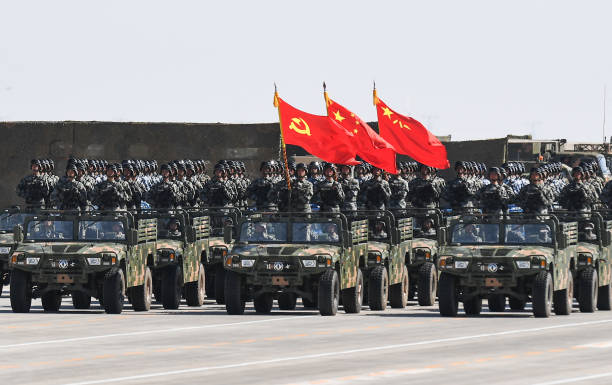
    THE PEOPLE’S LIBERATION ARMY, CHINA This army boasts of a standing combat strength of about 1.483 million and is the largest in the world, closely followed by India. The training regimen these men and women undergo in order to toughen them up is one that would make the average man and woman curl up in a corner after simply watching a video of it in practice.
    The members of this army are made to go through an obstacle course consisting of 17 steps which include, climbing, swimming and most terrifyingly, jumping over and in some cases, through flaming objects. You know they intend for you to be tough when they make you literally play with fire.
    Some people may read the description and shake their heads thinking, “Well, that doesn’t sound so tough”, well, let me tell you now that no matter how physically fit you are, the training is designed in a way to ensure that you really feel it. Potential recruits at one point of this training program, are made to submerge themselves below water for a complete one minute, and if they are to raise their heads even by accident, a superior is on standby to push it back in. Imagine going through such rigorous, physically tasking exercises and then depriving yourself of much-needed oxygen at a point, I am certain that you are starting to get the idea.
    You should note that in the year 2014, Chinese Special Forces units came out tops in the “Warrior Competition” which is an international competition between the Special Forces of various nations. So there is no doubt that they are one of the best and hardest special forces in the world.
    • 5. KOREAN SPECIAL WARFARE COMMAND:

    KOREAN SPECIAL WARFARE COMMAND
    KOREAN SPECIAL WARFARE COMMAND
    The trainees for this Special Forces unit are made to perform training exercises in extremely cold conditions, shirtless. They have to run, perform exercises like sit-ups, and even wrestle each other in those frigid conditions.
    The only time they seem to be allowed to wear tops is when they go to frozen rivers to engage in marksmanship training.
    • 6. ISRAELI SHAYETET 13:

    ISRAELI SHAYETET 13
    ISRAELI SHAYETET 13- one of the hardest special forces training in the world
    The best anti-terrorism unit in Israel is held to a very high standard of performance.
    The training period lasts about 20 months and they are made to go through training exercises in basically everything from demolitions, to paradrop operations and even diving under extremely frigid conditions with basically no visibility.
    Based on the area they excelled in, they are assigned to land, sea or air operations. It should be noted that before being officially welcomed into S13, the recruits have to go on actual coastal raiding missions. However, as a plus, a medical staff is always on the ground for both physical and psychological care which is no doubt always in high demand.
    The sea, air and land teams of the US Navy is probably one of the most famous groups on this list with the hardest special forces training in the world. The training lasts for 30 months on the average and includes something known as the “Hell week” which, true to its name, involves a heavy amount of agony compressed to last a week, during the first 3 weeks of training.
    Aspiring Navy SEALs are made to stay five and a half days in the cold, doing extreme exercises, performing training programs on coastal environments etc. all the while covered in mud and struggling with sleep because they are only allowed four hours of sleep.
    While they are going through hell, their trainers try to make them quit and mock them by eating donuts and taking coffee in front of them. There is always an emergency standby medical staff on the ground so, very few casualties are recorded.
    • 7. THE SPECIAL AIR SERVICE REGIMEN OF AUSTRALIA:

    Stuart Boner, in the year 2014, in collaboration with Robert Macklin, told the story of how he joined the Australian Special Air Service Regiment. There was one aspect of his story which had to do with training one to become resistant to interrogation. According to him, a white bag was placed over his head before he was stripped of his clothes and thrown in a cell where he was put in stressful positions for a long time without the option of sleep. It lasted for three days and when he attempted or even seemed to be dozing off, a slap was administered to wake him back up. He seemed to be of the opinion that he got PTSD from the experience.
    While they refuse to disclose their training methods, it was suggested by Harry Moffitt that there were more deaths recorded during the training process required to join, than during actual operations.
    The training process for Russian Spetsnaz is a long and staggering 5 years. The first five months out of those five years are designed specifically to break the recruits and the raise them up again, building them to the right state of mind and body to carry out the highly improvisational methods used by the unit.
    • 8. NATIONAL SECURITY GUARD COMMANDOS OF INDIA:

    One thing you would find common between these elite units is that their recruitment process usually involves making potential recruits pass through harsh, mostly unfamiliar territory and get to the base within a specified time, giving them a well-earned spot on among force with the hardest special forces training in the world. Many units within the Indian armed forces make use of these test and the men are given a day’s worth of food and water and made to take part in this test. Some recruits, as a way of impressing their superiors, try not to finish their rations before reaching the base.
    Trainers all have their various methods of toughening up recruits. A particular Italian trainer was notable for making potential recruits endure beatings from the locals as a means of testing their endurance. A different trainer had the recruits try to pass target practice while drunk in order to show them how it would be like, shooting under stressful conditions. The potential recruits who are able to endure this so-called ‘training’ are then allowed to join the Special Action Group, which is basically the elite out of the Indian elite.
    hardest special forces training in the world, world Most Difficult Special Force Training Programs in the World.

    Thursday, June 14, 2018

    June 14, 2018

    Market manipulation was key component in Bitcoin’s run

    According to a new paper by University of Texas finance professor John Griffin, and graduate student Amin Shams, Bitcoin’s price may have been artificially inflated in its run-up last December to nearly $20,000 per coin.

    It was just seven months ago that some of the internet’s most insufferable assholes told anyone that would listen about the newest force in the global currency market. It was a coin, made of digital 1’s and 0’s, that would disrupt the very idea of currency, a project so revolutionary that we’d all be rich, if only we had the resolve to “HODL.”
    And some did. During Bitcoin’s most recent boom, millionaires were made — a handful of billionaires too.

    Others bought at the peak of the hype cycle, mortgaging homes and other assets to get in early and ride the rocket to its next station, which was the “moon,” according to cryptocurrency types.
    Instead, they saw the asset falter. First losing half of its value in January, before a brief rally breathed new hope into the market, only to painfully extract it in the following weeks.

    Now, Bitcoin’s value sits at just $6,500, a nearly 70 percent decrease in value over that span. If this were a stock, this is the point at which shareholders might begin to consider liquidating assets.
    But in cryptocurrency, nothing is what it seems.

    According to Professor Griffin — who has a history of spotting fraud in financial markets — we were all victims in what could be a massive price manipulation scam.
    Griffin looked at the flow of digital tokens entering and leaving one of the largest cryptocurrency exchanges, Bitfinex, and identified several patterns that would suggest someone, or a group of people, had successfully propped up prices when they’d flattened at other exchanges.

    To push up the price when it sagged elsewhere, someone or some people, at Bitfinex purchased Bitcoin using a secondary currency known as Tether. Tether was created, and sold, by the owners of Bitfinex. Tether’s creators claim the currency is backed by the US dollar, providing a hedge against volatility in cryptocurrency markets. Simply put, it allowed investors to offload Bitcoin (or other cryptocurrencies) into Tether during wild price swings as a means to avoid substantial losses.

    Professor Griffin and Mr. Shams examined the flow of Tether and determined that roughly half of Bitcoin’s price in 2017 could be traced to the hours immediately following its movement into other exchanges — typically during periods where cryptocurrencies were in decline. Coin prices at marketplaces that used Tether exceeded those of exchanges that did not, according to the researchers. The pattern ended earlier this year when Bitfinex stopped issuing new Tether.

    Bitfinex executives have denied the exchange was involved in any manipulation. The company, told the New York Times today that it never engaged in “any sort” of market or price manipulation and that “Tether issuances cannot be used to prop up the price of Bitcoin or any other coin/token on Bitfinex.”

    Regulators don’t seem to be as sure. Late last year, the US Commodity Futures Trading Commission subpoenaed Bitfinex, and Tether — both of which share a CEO — for a closer look.
    Things got worse for the company from there, as it cut ties with a third-party auditor, Friedman LLP., over its failures in auditing the supply of Tether in a “reasonable timeframe.”

    Friedman, however, was never hired to look at the reliability of Tether’s records, just to prove that the stated amount existed — the equivalent of writing random numbers in an accounting ledger, and then hiring a firm to prove that there are numbers in an accounting ledger. The scope of Friedman’s audit was limited, and remains unfinished.

    According to the New York Times, two others have come forward to back Griffin’s research. University College London professor Sarah Meiklejohn said the analysis “seems sound” and chief economist at blockchain data analysis company Chainalysis, Phillip Gradwell, said the study “seems credible.”
    What this means for Bitfinex, Tether, or cryptocurrency markets as a whole remains to be seen.

    Wednesday, June 13, 2018

    June 13, 2018

    Yahoo Have Been Fined £250,000 By ICO Over Cyber-attack - Zeallbog

    Yahoo's UK arm has been fined £250,000 ($335,000) by the UK Information Commissioner's Office (ICO) over a data breach affecting more than 500 million users which took place in 2014.

    Yahoo have been fined over cyber attack - Zeallbog
    The firm said "state-sponsored" hackers had stolen personal information, which included names, emails, unencrypted security questions and answers.
    The ICO said Yahoo had failed to take appreciate measure to protect it. Yahoo said it did not comment on regulatory action. "The failings our investigation identified are not what we expect or will accept from a company processing significant volumes of personal data," wrote deputy commissioner of operations James Dipple-Johnstone in a blog.

    "Yahoo! UK Services Ltd had ample opportunity to implement appropriate measures, and potentially stop UK citizens' data being compromised."

    Around eight million of the affected accounts were believed to belong to people in the UK.

    The ICO's investigation also found:
      The firm failed to ensure that its Yahoo-owned data processor "complied with the appropriate data protection standards"
      It did not ensure that the credentials of employees with access to customer data were monitored
      There was "a long period of time" before the flaws which led to the breach were discovered or addressed

    Verizon acquired Yahoo in 2017 and combined it with AOL to form a company called Oath. The firm was investigated under the UK 1988 Data Protection Act which pre-dates the new European data regulation GDPR.

    Tony Pepper, CEO of Egress Software Technologies, said the data breach would go down in history as "one of the most notorious" - both because of its size and the two-year period between the attack and the report.

    "Although the fine has been a long time coming, I imagine there would be some sighs of relief that the investigation was carried out under the Data Protection Act, rather than the GDPR which has much tougher consequences for a breach," he said.

    Tuesday, June 12, 2018

    June 12, 2018

    Keep Mobile Phones Away From Your Body, It Can Cause Cancer

    Mobile phone have changed our life but also have negative impact on us.
    You must have read previous article that How mobile phone effect human body and health. In this article you will be came to know how mobile phone has changed human behaviour and effect to health and i had told you to publish an article on, "how mobile phone can cause cancer?" Lots of people have asked this question that "do mobile phone cause cancer or not?" People are afraid to use mobile phone for long hours.

    So today, we gonna discuss all about how mobile phone related to cancer and answer all questions that is it true that using mobile phone for long hours can cause cancer. You must have read many articles on this topic but still confused. But after reading this article you don't have to be worry about this topic and get all knowledge.Read full article to get proper knowledge.

    Do mobile phones cause cancer?
    When we talk about cancer from mobile phones the biggest term comes that is radiation. And its true only thing that can cause cancer from mobile phone is radiation. Okay its true that some kind of radiations can damage DNA that can lead to develop cancer. But cell phone does not give that kind of radiation.Cell phones give and receive signals with cell towers using a form of radiation known as radiofrequency(RF) radiation.

    Radiation is type of electromagnetic energy. Just think electromagnetic radiation as a wave, with certain frequency based on its energy. It is of 2 types:
    Ionizing radiation: Electromagnetic energy that can knock out electrons is called ionizing radiation. and it can chemical bond's in your cells and damage DNA.It can cause cancer.
    NON-Ionizing radiation: Electromagnetic energy doesn't have a high enough frequency to break chemical bonds is called non-ionizing radiation.It cannot knock out electrons from an atom. It can't cause cancer. Lower the frequency less the chances of cancer and higher the frequency higher the chances of cancer.
    Ionizing radiation - Zeallbog 

    Every country have lower the SAR value of mobile phone.
    What is SAR value? Specific Absorption Rate (SAR) is a guideline created to measure the rate that body tissue absorbs radiation during cell phone use . The SAR for cell phone radiation was set at a maximum of 1.6 watts of energy absorbed per kilogram of body weight.


    Now we can say that mobile phone cannot cause cancer but in case of brain cancer here we have to keep some points in mind. Studies showed that it can cause two types of brain caner gliomas and acoustic neuromas. Gliomas – a type of tumor that starts in the brain or spine are typically malignant and they are particularly deadly.


    Acoustic neuromas – though non-malignant (low-grade cancer), are in many cases life threatening given that they are an intracranial (within the skull) tumor. Longs hours on calling or phone kept near head can cause these types of cancer. But its only studies not proved. But we should take measures and precautions.That are: Don't use more than half hour a day on calling if so use earphones(but not bluetooth earphones). Avoid making calls with your phone on your ear, make use of earphones instead. Put your phone on airplane mode when you don't need it so much, don't take your phone to your bedroom at night or put your phone at air plane mode or put your phone far from your head.
    Don't carry mobile phone in your pocket when not necessary.

    In world more than 5 billion people are using mobile phones and making calls. I don't think even a million of people has got cancer from mobile phone. If mobile phone really hazardous for human being our government must have taken some actions as like tabacoo or cigarette. So, you don't have to be worried about this. People do use mobile phones for 15 years and they go about daily with phone in hands, and to their ears when making calls and they are still healthy. You just have to take some precaution and nothing more. Just live your life comfortably and if you want to worry take worry of cigarette that really hazard to health.

    Tuesday, May 29, 2018

    May 29, 2018

    Lawmakers Needs To Restructure Their Regulatory Mode Of Big Techs

    GDPR - Zeallbog 

    If members of the European Parliament thought they could bring Mark Zuckerberg to heel with his recent appearance, they underestimated the enormous gulf between 21st century companies and their last-century regulators.

    Zuckerberg himself reiterated that regulation is necessary, provided it is the “regulation".
    But anyone who thinks that our existing regulatory tools can reign in our digital behemoths is engaging in magical thinking. Getting to “right regulation” will require us to think very differently.

    The challenge goes far beyond Facebook and other social media: the use and abuse of data is going to be the defining feature of just about every company on the planet as we enter the age of machine learning and autonomous systems.
    So far, Europe has taken a much more aggressive regulatory approach than anything the US was contemplating before or since Zuckerberg’s testimony.

    The European Parliament’s Global Data Protection Regulation (GDPR) is now in force, which extends data privacy rights to all European citizens regardless of whether their data is processed by companies within the EU or beyond.
    But I’m not holding my breath that the GDPR will get us very far on the massive regulatory challenge we face. It is just more of the same when it comes to regulation in the modern economy: a lot of ambiguous costly-to-interpret words and procedures on paper that are outmatched by rapidly evolving digital global technologies.

    Crucially, the GDPR still relies heavily on the outmoded technology of user choice and consent, the main result of which has seen almost everyone in Europe (and beyond) inundated with emails asking them to reconfirm permission to keep their data. But this is an illusion of choice, just as it is when we are ostensibly given the option to decide whether to agree to terms set by large corporations in standardized take-it-or-leave-it click-to-agree documents.  

    There’s also the problem of actually tracking whether companies are complying. It is likely that the regulation of online activity requires yet more technology, such as blockchain and AI-powered monitoring systems, to track data usage and implement smart contract terms.

    As the EU has already discovered with the right to be forgotten, however, governments lack the technological resources needed to enforce these rights. Search engines are required to serve as their own judge and jury in the first instance; Google at last count was doing 500 a day.

    The fundamental challenge we face, here and throughout the modern economy, is not: “what should the rules for Facebook be?” but rather, “how can we can innovate new ways to regulate effectively in the global digital age?”


    The answer is that we need to find ways to harness the same ingenuity and drive that built Facebook to build the regulatory systems of the digital age. One way to do this is with what I call “super-regulation” which involves developing a market for licensed private regulators that serve two masters: achieving regulatory targets set by governments but also facing the market incentive to compete for business by innovating more cost-effective ways to do that.  

    Imagine, for example, if instead of drafting a detailed 261-page law like the EU did, a government instead settled on the principles of data protection, based on core values, such as privacy and user control.

    Private entities, profit and non-profit, could apply to a government oversight agency for a license to provide data regulatory services to companies like Facebook, showing that their regulatory approach is effective in achieving these legislative principles.  
    These private regulators might use technology, big-data analysis, and machine learning to do that. They might also figure out how to communicate simple options to people, in the same way that the developers of our smartphone figured that out. They might develop effective schemes to audit and test whether their systems are working—on pain of losing their license to regulate.

    There could be many such regulators among which both consumers and Facebook could choose: some could even specialize in offering packages of data management attributes that would appeal to certain demographics – from the people who want to be invisible online, to those who want their every move documented on social media.
    The key here is competition: for-profit and non-profit private regulators compete to attract money and brains the problem of how to regulate complex systems like data creation and processing.

    Zuckerberg thinks there’s some kind of “right” regulation possible for the digital world. I believe him; I just don’t think governments alone can invent it. Ideally, some next generation college kid would be staying up late trying to invent it in his or her dorm room.

    The challenge we face is not how to get governments to write better laws; it’s how to get them to create the right conditions for the continued innovation necessary for new and effective regulatory systems.

    Sunday, May 27, 2018

    May 27, 2018

    5 Ways Deception Tech Is Interrupting Cyber Security


    Enterprises and their Security Operations Centers (SOCs) are under siege. Security events are being triggered from all corners of the security stack – from the firewall, endpoints, and servers, from intrusion detection systems and other security solutions. What’s more is that security teams do not have enough people or hours in a day to analyze the alerts that are coming in, and most ‘security events’ don’t even imply an attack in progress. They often are simply sharing information (failed connections, for example) or are what we call ‘false positives’ (when a solution thinks it has found a specific vulnerability, but in fact, it hasn’t.) 

    “Europe's leading digital technology conference”

    It's happening, Join 15k digital minds to shape what's next for your business
      This is important because today, attackers use stealthy tactics that leverage these security challenges – after infecting an asset inside an organization, they keep a low profile, moving laterally in the hunt for valuable, sensitive data. The longer they stay in the network, the harder it becomes to detect their trail. The average ‘dwell time’ – how long an attacker or malicious insider is inside an organization’s network – is measured in months, with some estimates in the 200+ day range. That’s why it’s critical for organizations – both large and small – to focus their cybersecurity strategy on earlier detection and faster response. One of the technologies trend that is promising to do this, is deception.

    What is deception technology?

    Sun Tzu said it best in his book on The Art of War: “All warfare is based on deception.” ‘Deception’ is a classic tactic used in warfare, both for protection and as a mechanism to attack enemies. One of the best-known deception operations conducted during World War II was when the British deceived the Germans in Operation Mincemeat, which preceded the invasion of Sicily. This was a classic operation of planting strategic misinformation in order to deceive the enemy and distract them from the real place where the attack actually took place. The idea behind a cyber deception strategy is similar. Organizations often know to varying degrees what the attackers are looking for, what they expect to find, and how they might attack and use the information they find – so why not use this against them? The ultimate goal of deception is to lure attackers to ‘decoy’ assets that look and feel real but aren’t. This can be done through different methods including traps in the network, on the endpoints and servers, data traps, and more. By engaging with the decoy or deception environment, attackers or malicious insiders essentially reveal themselves to the organization – but they don’t know it.

    5 ways deception is changing the cybersecurity landscape

    Often people hear ‘deception’ and they immediately think of ‘honeypots’ – which is basically a static decoy that imitates a simple computer system and does nothing unless an attacker stumbles across it. However, deception technology has greatly improved beyond the honeypot concept today. How? By being active – both in luring and baiting attackers to a deception environment, as well as in the decoys. Here are five ways deception technology is changing the cybersecurity landscape:

    1. Maximum accuracy with minimal human investment

    When a deception solution triggers an alert, organizations know it is an accurate incident no matter what – goodbye false positives! Any access to the deception layer is by definition malicious and the security team has to investigate it immediately. With cybersecurity teams struggling to focus on real threats due to all the “noise” that is generated from the multiple layers of security tools and the lack of personnel to physically triage and investigate each alert.

    2. Get personal with your business

    Deception has taken the honeypot concept to another level. It structurally learns and adapts to your organization’s network and cloud environments. Decoys change to match the real environment as it changes. Additionally, solutions that use ‘breadcrumbs’ can strategically lure attackers and malicious insiders to the decoys. This ‘personalization’ is critical to a modern deception defense – to ensure that the deception components always look and feel real to bad guys.

    3. Ensure a post-breach defense for any type of attack

    Cyber attacks come in many forms. Deception provides a post-breach defense that is agnostic to the type of attack. Whether the attack is by spear phishing, drive-by download, or comes through from a connected device, deception lets you know there is someone inside your network looking to steal data.

    4. Triggers threat hunting operations

    Threat hunting exists in only the largest, most mature security organizations. But even smaller companies can make this highly advantageous strategy work with deception. Deception provides the first true signal of an infected asset that a threat hunter can use to quickly begin the investigation process.

    5. Empowers organizations towards strategy and active defense

    Traditional security attempts to block and prevent threats. It’s a constant game of cat-and-mouse. Deception changes this game by giving defenders the ability to learn about attackers in a similar manner that attackers try to learn about their targets. Once they know an attacker is in the network, they can observe their behaviors and patterns. This intel helps security teams better understand what attackers are after and the best way to respond.

    Finally

    While prevention defenses are certainly still needed, it’s clear that advanced threats still have too much success. Early detection is now more critical than ever. Every business needs to be strategizing about how they plan to fill the detection to infection gap. There are several vendors offering deception, including Fidelis Cybersecurity, Trapx, Attivo and Illusive Networks. Deception is one technology that can significantly reduce dwell time. On top of this it is easy to install, does not require a lot of resources to manage, and it increases the effectiveness and the efficiency of security teams. For companies considering this technology, deception should be tightly integrated not only with the SIEM but also with endpoint solutions (EDR/ EPP) and with network security solutions to ensure a pre- and post-breach defense that strengthens the security posture of the organization.

    Saturday, May 26, 2018

    May 26, 2018

    Apple Is Offering A $50 Credit ToUsers Who Paid For A New iPhone Battery Last Year

    Sometime early this year, Apple announced to explore the possibility of offering partial refunds to select customers who purchased a replacement battery prior to the launch of its discounted battery replacement program.
    On Wednesday, Apple announced a credit for out-of-warranty iPhone battery replacements.

    Customers who paid for an out-of-warranty battery replacement for the iPhone 6 or later devices between January 1, 2017, and December 28, 2017, may be eligible to receive a $50 credit. Apple defines eligible battery replacements as those that were completed at an authorized Apple service location – either at an Apple Store, an Apple Repair Center or an Apple Authorized Service Provider.

    Apple says eligible customers will be contacted via e-mail between May 23, 2018, to July 27, 2018, with instructions on how to obtain the credit. If you believe you are eligible for a credit but don’t hear from Apple by August 1, 2018, you’re encouraged to contact Apple regarding the matter. Note that you may have to provide proof of purchase to secure the refund.

    According to source, the said credit will arrive as an electronic funds transfer or a credit on the credit card used to pay for the battery replacement.
    In-warranty iPhone battery replacement customers are not eligible for the credit, Apple says.

    Apple announced a price reduction for out-of-warranty battery replacements on the iPhone 6 and newer late last year, slashing the price down to $29 following a major controversy over CPU throttling.